A skill can pass every security scanner you own and still teach an agent
to work badly. Crucible audits the methodology, not just the safety —
deterministically, with evidence attached to every claim.
People are installing hundreds of third-party "skills" into their
agents. Security scanners catch malware, secrets, injection — the loud
failure. They have nothing to say about the quiet one: an instruction
that passes every scanner and still teaches an agent to work badly.
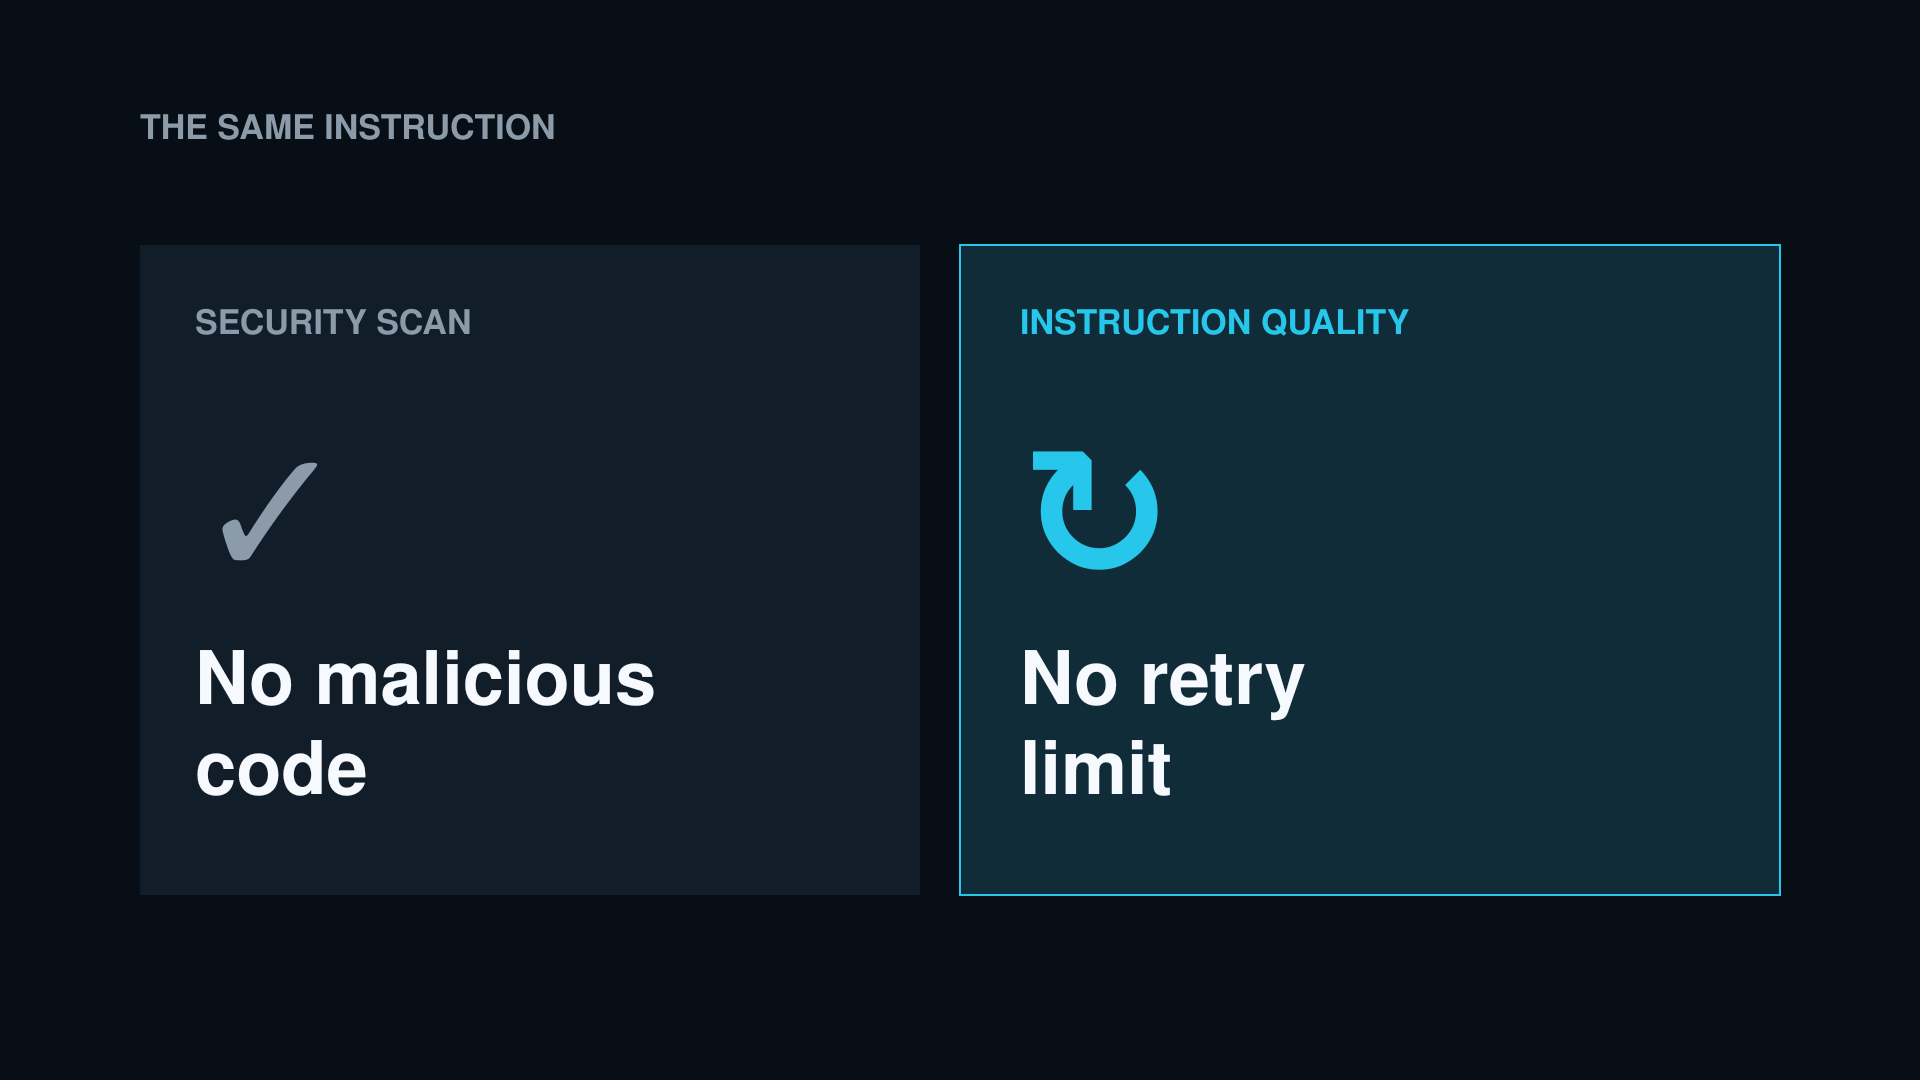
A perfectly safe skill
---
name: retry-example
description: Retry failed operations.
---
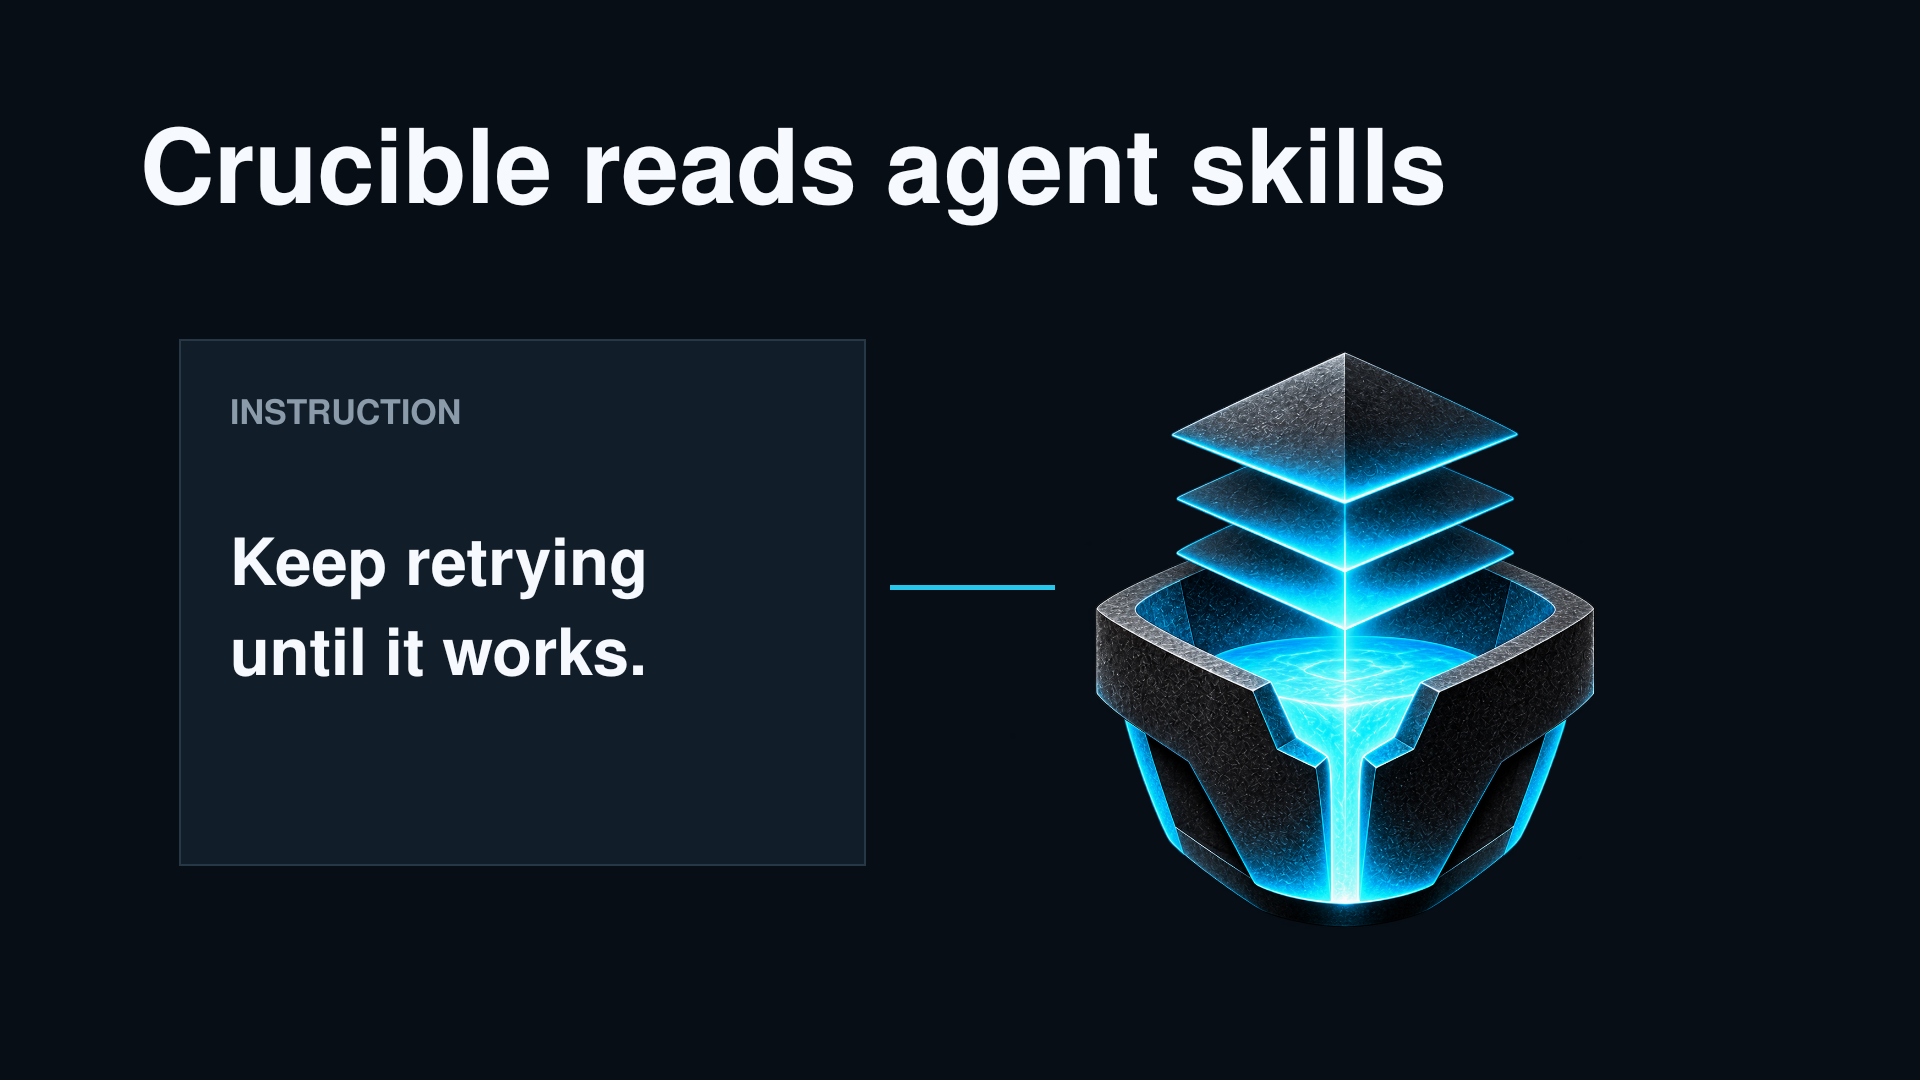
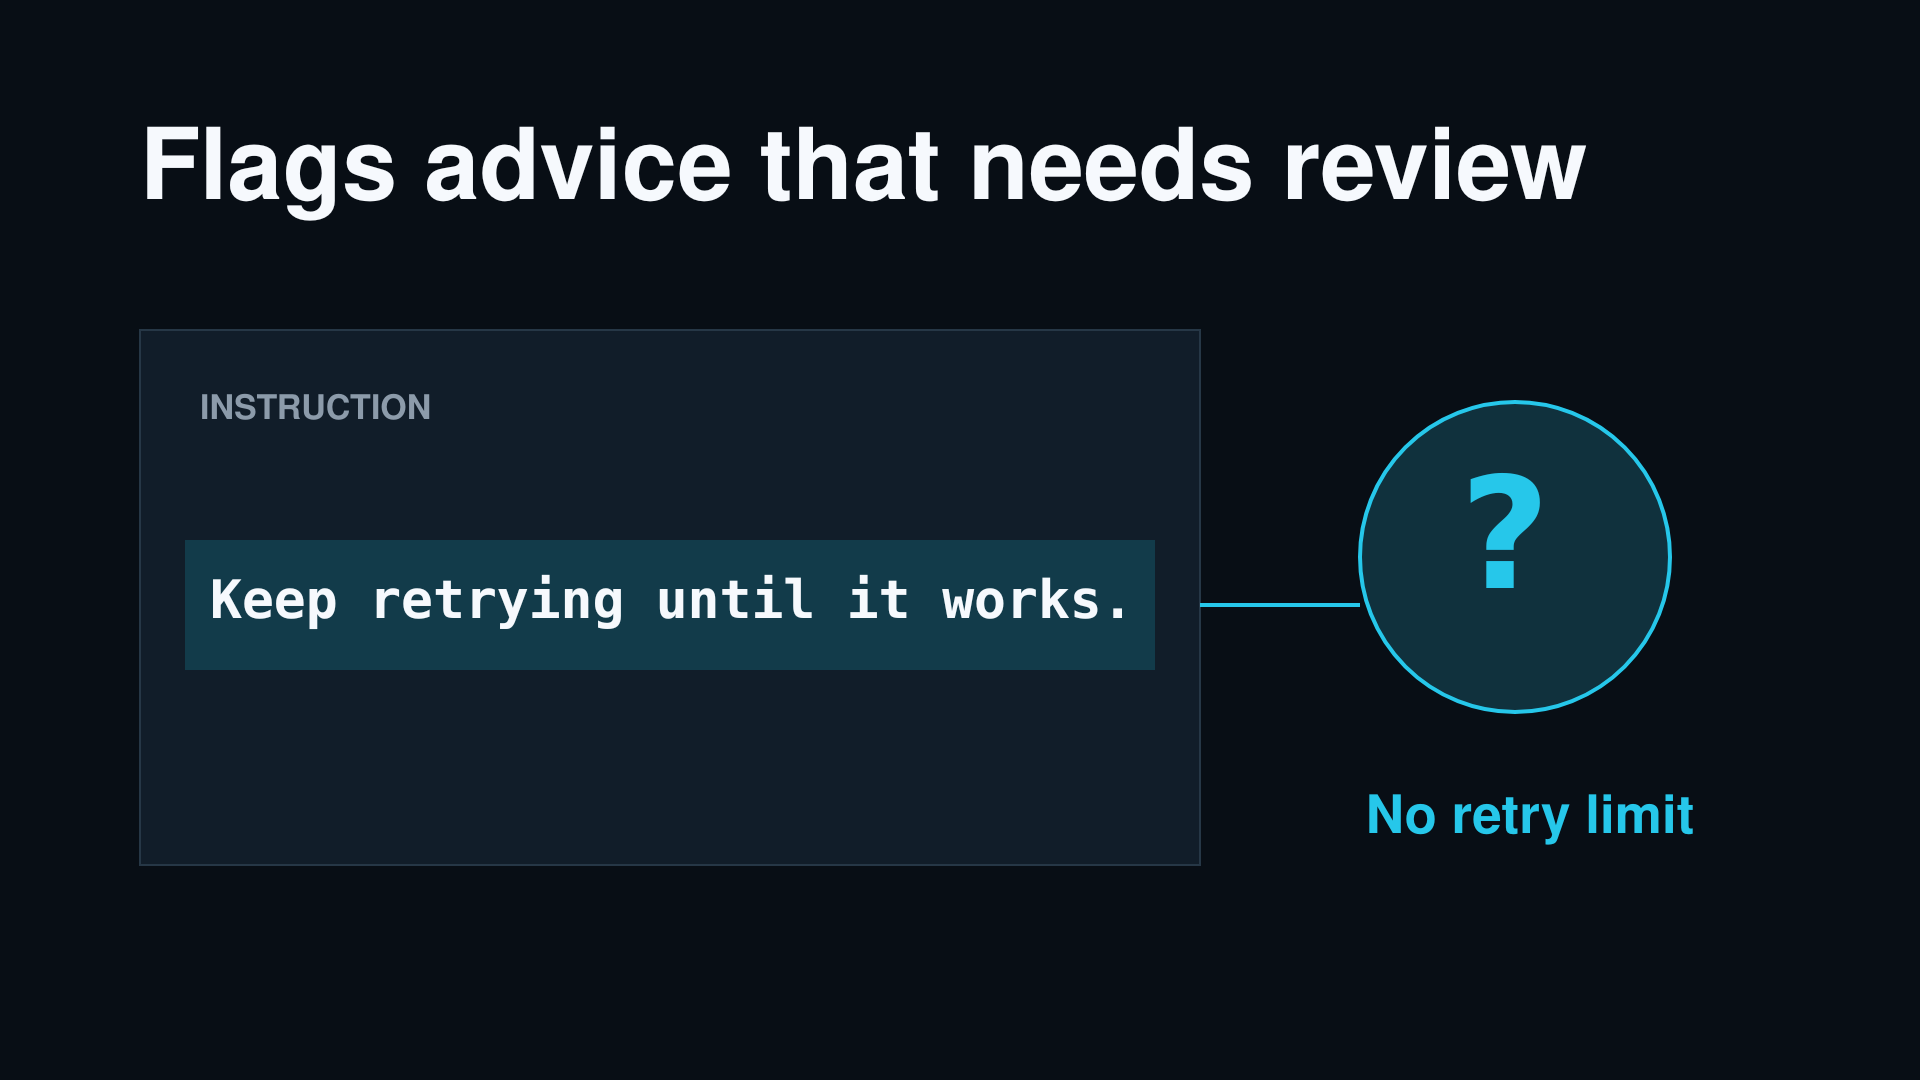
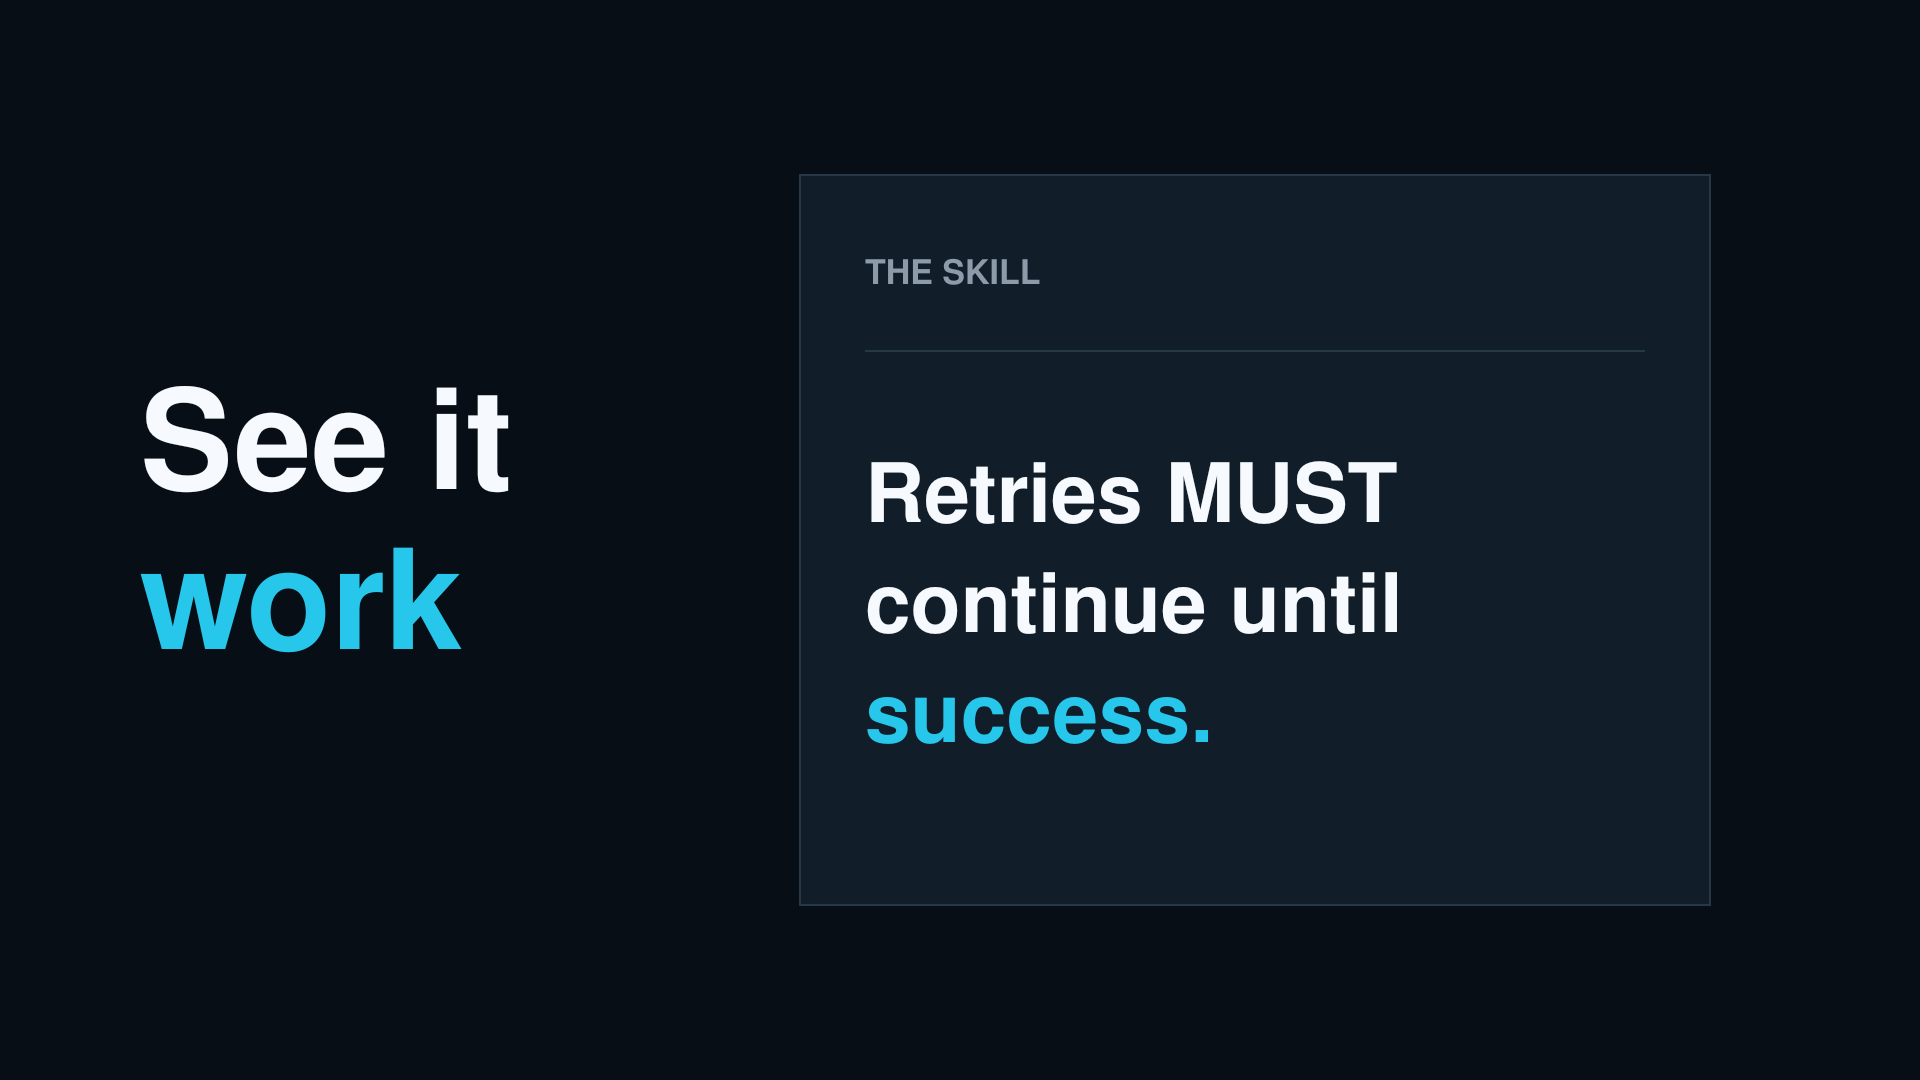
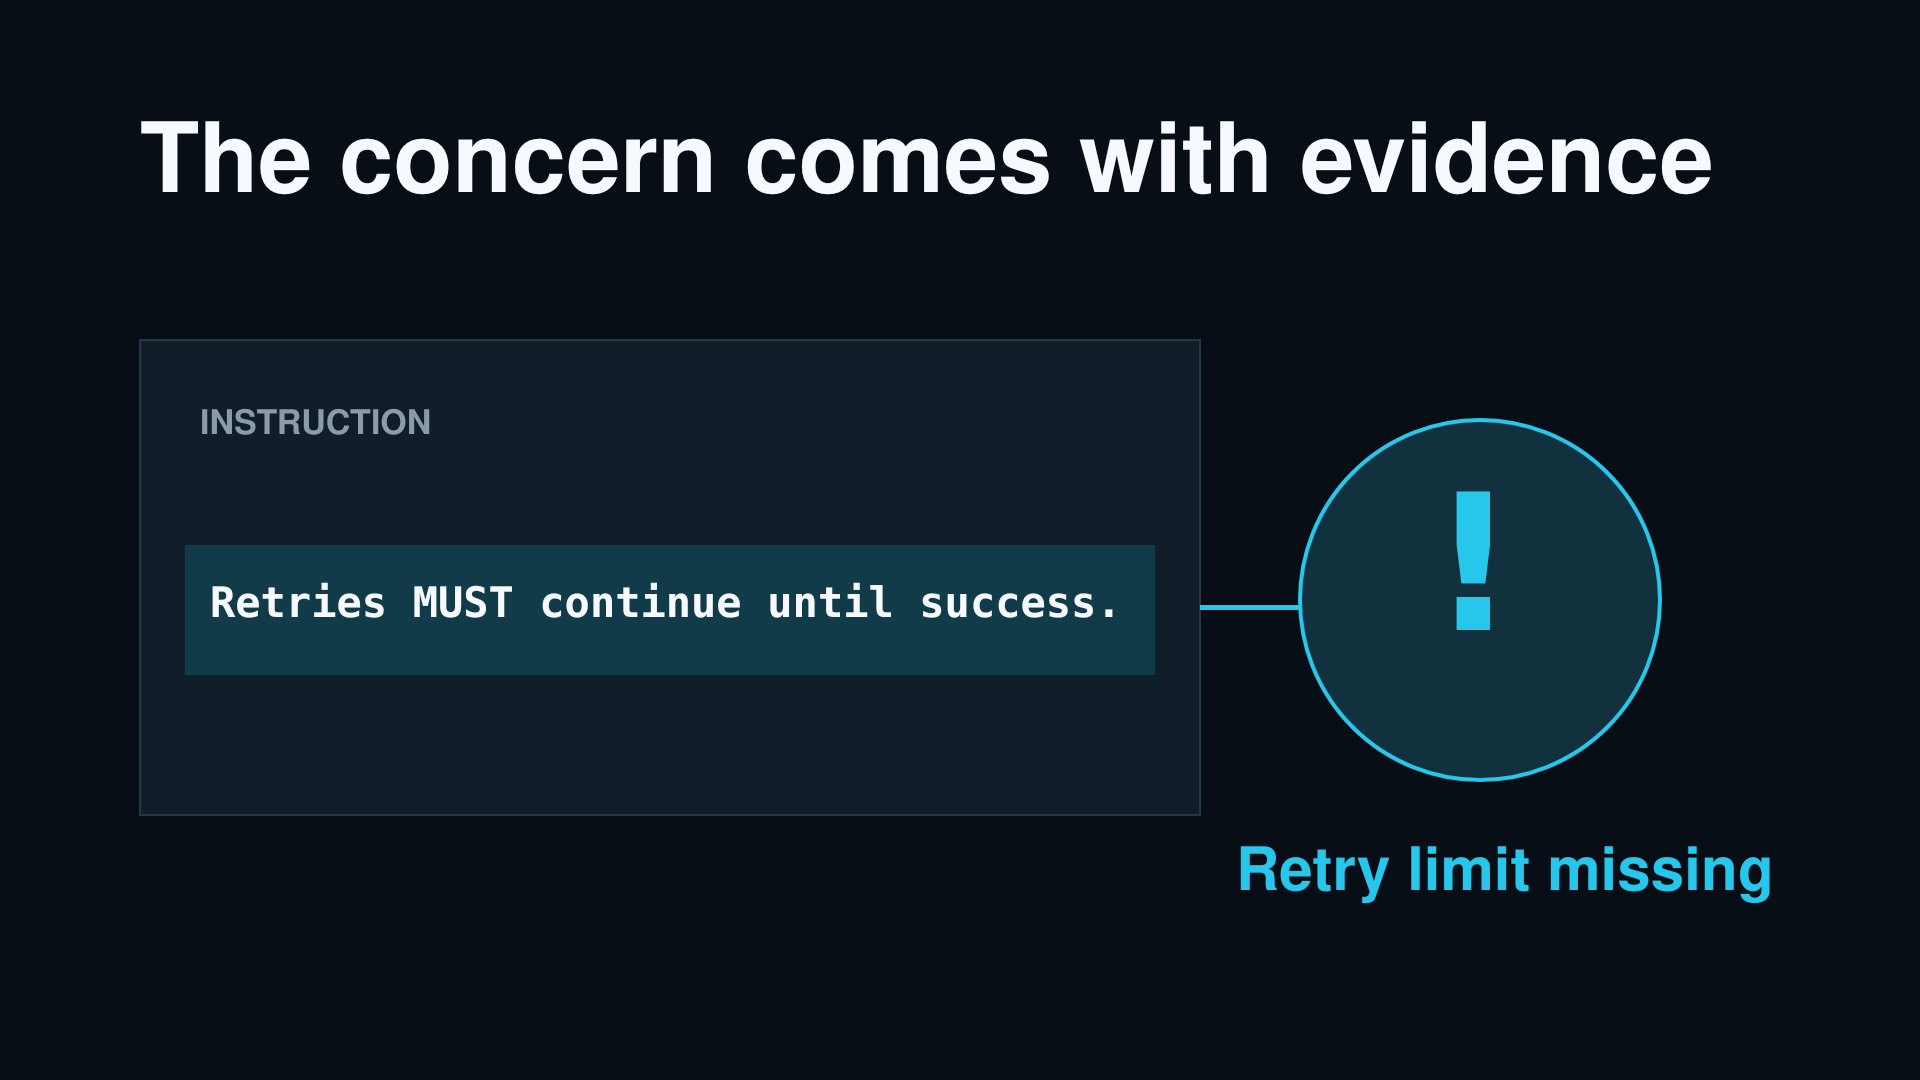
Retries MUST continue until success.
What it actually does
✅ No malware
✅ No exposed secret
✅ No prompt injection
✅ Passes every security scanner
And it tells an agent to retry forever — no
bound, no way to check the obligation it just declared. Nobody
attacked anything. Someone wrote a bad methodology, and an agent
believed it.
How Crucible works
The model proposes. A deterministic gate decides.
Crucible compiles a skill's declared methodology into source-addressable
records and audits them deterministically. A model may propose a merge,
a repair, a second opinion — but a deterministic gate accepts or
refuses. We proved this directly: the same merge, run twice at
temperature zero, produced two differently-worded skills from the model
and the exact same verdict from the gate, both times.
Skill text
→
Deterministic auditor
→
Sealed findings (SHA-256)
Model (proposes)
→
Deterministic gate
→
Accept / Refuse
Powered by NVIDIA Nemotron 3 Super 120Bvia Nebius Token Factory
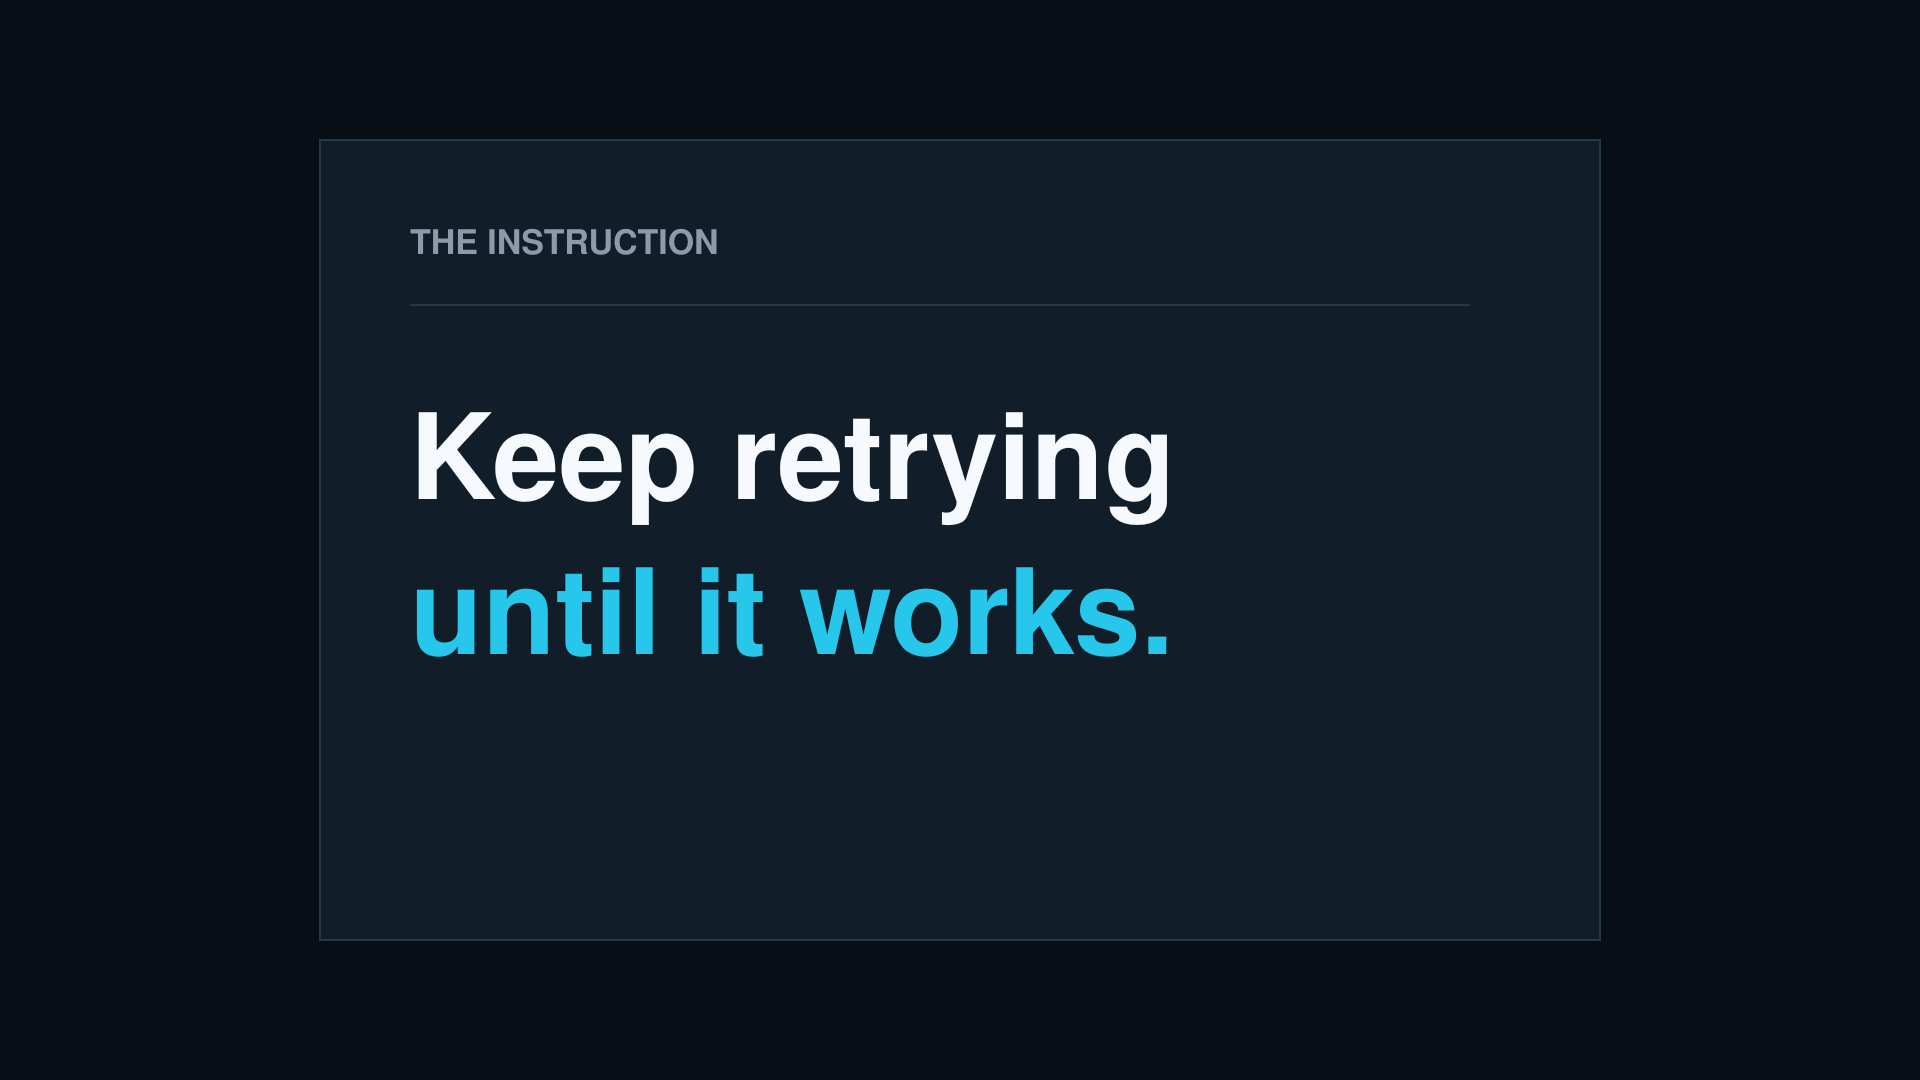
This is the actual scanner, run against the author's own installed
skills — not a mockup. Use the same interface live →
Measured, not asserted
We ran it where it could actually fail.
Four external corpora, written by people who have never seen this
project. Two of them frozen and held back so the detector could not be
tuned to flatter itself.
2,806
skills audited across five corpora
337 / 337
duplicate findings checked — every one a true positive
963
tests passing
Reading our own audit output with the same discipline we apply to
everyone else's, we found our own demo page had been silently wrong — it
claimed every check passed when several had simply had nothing to
examine. We fixed it to say so honestly instead of letting silence read
as clean.
Demo
See it in action.
Three minutes, no cuts skipped: the problem, the architecture, a real
audit run live. Or skip the video and try the real
audit engine yourself →
Slides
The full pitch deck.
24 slides, same story as the video. Scroll sideways, or click any slide
to view it full size.